Database Availability Group (DAG) in Exchange 2010

One of the new features of Exchange 2010 is DAG Database Availability Group. The Customer were i work now wants Exchange 2010 in a dag cluster because they have a datacenter for failback.
Because i going to implement Exchange 2010 at the customer i created a test setup.

Configuration:

Server 1 – HYPERVDC-01
OS: Microsoft Windows 2008 R2 Standard x64
IP: 192.168.150.90
Roles: Active Directory / Hyper-V

Server 2 – CHEK10-01
OS: Microsoft Windows 2008 R2 Standard x64
IP: 192.168.150.91
Roles: Exchange 2010 HT / CAS

Server 3 – CHEK10-02
OS: Microsoft Windows 2008 R2 Standard x64
IP: 192.168.150.92
Roles: Exchange 2010 HT / CAS

Server 4 – DAGEK10-01
OS: Microsoft Windows 2008 R2 Enterprise x64
IP: 192.168.150.93
Roles: Exchange 2010 MBX

Server 5 – DAGEK10-02
OS: Microsoft Windows 2008 R2 Enterprise x64
IP: 192.168.150.94
Roles: Exchange 2010 MBX

Creating the DAG

clip_image002
clip_image004

Groupname: DAG01
Witness Server: CHKEK10-01 (Microsoft says use one of the CAS or Hub Servers. You cannot use a DAG Server! If you want use a non Exchange 2010 server you must at the Exchange Trusted Subsystem group at the local administrators group.
Witness Directory: C:\DAG01
clip_image006

Add a MB server to a DAG

clip_image008clip_image010

clip_image012clip_image014

clip_image016clip_image018

clip_image020

Setting a IP address on a Database Availability Group

With the following command you can set the DAG Database Availability Group an IP address. Set-DatabaseAvailabilityGroup -Identity DAG01 -DatabaseAvailabilityGroupIpAddresses 192.168.150.96

Checking Microsoft Office 2010 KMS Activation Status

Before you start you must al ready have a kms server.
On the KMS server you need to install the Office 2010 KMS Host License Pack on the KMS Server.
Launch Microsoft Outlook 2010
Click to the File tab. Click Help.

Office is not activated
clip_image002
Determining Which Activation Method Office is Using – KMS or MAK

Click the start menu and enter cmd /k cscript “%programfiles%\Microsoft Office\Office14\ospp.vbs” /dstatus in the search box.

If running 32 bit Office 2010 on 64 bit Windows, %programfiles% above should be replaced with %programfiles(x86)%.

Not Activated

clip_image004

Checking if a DNS Domain is Configured for KMS Auto-Discovery

To check if a DNS domain is configured for KMS auto-discovery, check that a SRV record exists.

nslookup -type=srv _vlmcs._tcp.wardvissers.nl

If a SRV record exists for the domain, the DNS server will detail the SRV record.


C:\>nslookup -type=srv _vlmcs._tcp

Server:  ward-dc02.wardvissers.local

Address:  192.168.150.6

Non-authoritative answer:

_vlmcs._tcp.wardvissers.local SRV service location:

          priority       = 0

          weight         = 0

          port           = 1688

          svr hostname   = ward-dc2.wardvissers.local

If no SRV record exists for the domain, the DNS server will return an error

Verifying that a Windows Computer can Communicate with the KMS Activation Server

KMS activation requires that the machine to be activated has TCP port 1688 open for outbound communication to the activation server.

Verifying that outbound TCP port 1688 is open to the KMS server

  1. Download and install the utility portqry.exe from Microsoft. It is a command line utility from Microsoft that reports the port status of a remote host.
  2. From a command prompt, run the command:

portqry.exe -n ward-dc02.wardvissers.local -p tcp -e 1688

The command will return “TCP port 1688 (unknown service): LISTENING” if the computer is able to communicate with the KMS server.

clip_image006

If the command returns “TCP port 1688 (unknown service): FILTERED” then the computer is unable to communicate with the KMS server

Manually Specifying the KMS Activation Server

1. Type cmd in the search bar to locate the command window..
2. At the command prompt, type cd\Program Files\Microsoft Office\Office14.

If running 32 bit Office 2010 on 64 bit Windows, Program Files above should be replaced with Program Files (x86).
Run the command cscript ospp.vbs /sethst:ward-dc02.wardvissers.local to manually specify the KMS activation server.
clip_image007

Run the command cscript ospp.vbs /act to activate Office with the KMS server.

clip_image007[1]

Launch Microsoft Outlook 2010 agein
Click to the File tab. Click Help.

Office is activated

clip_image001

Where to find the right MDT 2010 logs

Each MDT 2010 script automatically creates log files during its execution. The names of these log files match the name of the script—for example, ZTIGather.wsf creates a log file named ZTIGather.log. Each script also updates a common master log file (BDD.log) that aggregates the contents of the log files that MDT 2010 scripts create. MDT 2010 log files reside in C:\MININT\SMSOSD\OSDLOGS during the deployment process. Depending on the type of deployment being conducted, the log files are moved at the completion of the deployment to either %WINDIR%\SMSOSD or %WINDIR%\TEMP\SMSOSD. For Lite Touch Installation (LTI) deployments, the logs start in C:\MININT\SMSOSD\OSDLogs. They end up in %WINDIR%\TEMP\DeploymentLogs when task sequence execution is complete.

MDT 2010 creates the following log files:

BDD.log: This is the aggregated MDT 2010 log file that is copied to a network location at the end of the deployment if you specify the SLShare property in the Customsettings.ini file.

LiteTouch.log: This file is created during LTI deployments. It resides in %WINDIR%\TEMP\DeploymentLogs unless you specify the /debug:true option.

Scriptname.log: This file is created by each MDT 2010 script. Scriptname represents the name of the script in question.

SMSTS.log: This file is created by the Task Sequencer and describes all Task Sequencer transactions. Depending on the deployment scenario, it may reside in %TEMP%, %WINDIR%\System32\ccm\logs, or C:\_SMSTaskSequence, or C:\SMSTSLog.

Wizard.log: The deployment wizards create and update this file. 

WPEinit.log: This file is created during the Windows PE initialization process and is useful for troubleshooting errors encountered while starting Windows PE.

DeploymentWorkbench_id.log: This log file is created in the %temp% folder when you specify a /debug when starting the Deployment Workbench.

Configuring Client Access Array for Exchange 2010

When you want to use the Client Access Array function from Exchange 2010. You have to options.
1. Use the NLB function in Windows. Check this article that i blogged: Configuring NLB for Exchange 2010 for Cas load balancing.
2. When you have 2 physical load balancers in combination with a DAG cluster.

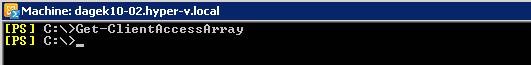
I haven’t any pre-Created CAS arrays in my hyper-v.local domain. But you would to check of there is any pre-created CAS Arrays. Run the command below. if you didn’t create a CAS Array before, you will get nothing .

Get-ClientAccessArray
clip_image002

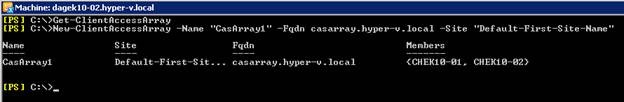
Then you should create new Client Access Array. Run below Cmdlet in Exchange Management Console

New-ClientAccessArray –Name “CasArray1” –Fqdn casarray.hyper-v.local -Site “Default-First-Site-Name”

clip_image004
Now we have finished creating a CAS array. Then we must associate databases with this CAS Array.
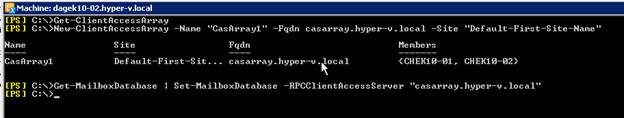
Use below CMDLet to add mailbox database to CAS array. We can attach all mailbox databases at once as shown as shown  below

Get-MailboxDatabase | Set-MailboxDatabase -RPCClientAccessServer “casarray.hyper-v.local”
clip_image006

Configuring NLB for Exchange 2010 for CAS Load Balancing

Exchange’s dependence on the Client Access Server (CAS) role has increased dramatically in Exchange 2010.  This is because, in Exchange 2010, on-network Outlook MAPI connectivity now connects to a mailbox through the CAS role via the RPC Client Access Service.  As a result, high availability of the CAS role is crucial since any failure of CAS could affect Outlook client connectivity.  For smaller implementations or those where the limitations of native Windows Network Load Balancing (NLB) are not a major problem

You need two or more Exchange 2010 servers (each with two NICs) with the CAS role installed have been deployed, you are ready to start configuring NLB to provide high availability and load balancing.  First, you must allocate a dedicated private IP address and create an associated A record in DNS for the NLB cluster. 

This IP address and name are what clients will connect to and against which the ClientAccessArray will be created.  In this blog post, I will use 192.168.150.95 and casarray.hyper-v.local
To simplify the management of your NLB cluster members, I recommend that you name each NIC’s network connection so that it is easy to understand what function the NIC serves.  For example, as depicted below, I have named the connections “LAN” (used for communication with clients and servers on the network) and “NLB” (used for internal NLB heartbeat).  This process should be repeated on all NLB cluster members.

IP configuration:
Server 1:
LAN:
IP: 192.168.150.90
Subnetmask: 255.255.255.0
Gateway: 192.168.150.254
DNS: 192.168.150.1

Server 2:
LAN:
IP: 192.168.150.91
Subnetmask: 255.255.255.0
Gateway: 192.168.150.254
DNS: 192.168.150.1
clip_image002


Configuring NLB – First Member

On each NLB cluster member, NLB must be installed.  With Windows 2008 R2, this can be completed simply by running the command “ServerManagerCmd -i NLB” via a command prompt.  Once NLB has been installed, launch the Network Load Balancing Manager to continue the configuration process.

clip_image003[1]

To create your new cluster, you can right-click Network Load Balancing Clusters or simply click Cluster, New.  In the New Cluster wizard, enter the name of the first server in the NLB cluster (for example, CHEK10-01) and click Connect.  This will display the available NICs on the server, at which point the NLB NIC should be chosen before clicking Next.

clip_image005

Since this is the first member of the NLB cluster, you can leave the all of the Host Parameters at their default values, as depicted below.  Please note that the Priority value should be configured as 1 for the first member.

clip_image007

Next we must configure the IP address and subnet mask of the NLB cluster, which is the IP address for which we created a DNS A record at the very beginning of this process.  In this example, this would be 192.168.150.95 and 255.255.255.0, respectively.

clip_image009

For the Cluster Parameters, we want to enter the FQDN of the DNS A record we created at the very beginning of this process (casarray.hyper-v.local).  In addition, Unicast should be selected as the desired clustered operation mode.

clip_image011

I lieve the Port Rules how they are and end with Finish
clip_image013

Let the NLB cluster converge with its first member and you should eventually see the cluster report success.

clip_image015[1]

Now you can proceed with adding your second cluster member.

Configuring NLB – Second/Subsequent Member

After the configuration of the NLB cluster itself and the first NLB cluster member has been completed, you are ready to add additional members.  Provided that NLB has been installed, you can simply right-click on your NLB cluster in the Network Load Balancing Manager and click Add Host To Cluster.

Enter the name of the second NLB cluster member, for example CHEK10-02, and click Connect.  Be sure to choose the NLB LAN NIC and click Next.

clip_image017

On the Host Parameters screen, ensure that the Priority is set to 2 (or as appropriate, depending on how many cluster members you have) and click Next.

clip_image019

Confirm that your port rules are accurate and, if they are, click Finish to add your second NLB cluster member.

clip_image021

Let the NLB cluster converge with the new member and, eventually, it should report success.

clip_image023

At this point, you have an NLB cluster with two members!

Next configure CASARRAY.

Access Denied Error 0x80070005 message when initializing TPM for Bitlocker

When you try to turn on Bitlocker on Windows 7 Operating System Drive, you may get the Access Denied Error message while initializing TPM.

image

Additionally, when you open the TPM Management Console and you try to initialize TPM you get error message 0x80070005.

image

Solution:

To set correct permissions, follow the instruction below:

1. Open Active Directory Users and Computers.

2. Select the OU where you have all computers which will have Bitlocker turned ON.

3. Right Click on the OU and click Delegate Control.

image

4. Click Next and then click Add.

image

image

5. Type SELF as the Object Name.

image

6. Select create a custom task to delegate.

image

7. From the object in the folder, select Computer Objects.

image

8. Under show these permissions, select all 3 checkbox.

image

9. Scroll down in permissions and select the attribute Write msTPM-OwnerInformation.

image

10. Click Finish.
image

After you have done the above steps, you should be able to initialize TPM successfully.

It worked for me!!!

SOURCE

Windows Server 2008 R2: Hyper-V Component Architecture Poster

The Hyper V documentation team has done a great job of putting together a detailed Windows Server 2008 R2: Hyper-V Component Architecture Poster.  Download the .PDFimage

The poster provides details on the inner workings of things like:

  • Virtual Networking
  • Virtual Storage
  • Live Migration
  • Virtual Machine Snapshots
  • Virtual Machine File Management

VMware Workstation 7.1 is available

VMWare has released VMware Workstation 7.1.

image

What’s New in VMware Workstation 7.1

  • Support for 8 virtual processors (or 8 virtual cores) and 2 TB virtual disks.
  • Support for OpenGL 2.1 for Windows Vista and Windows 7 guests.
  • Greatly improved DirectX 9.0 graphics performance for Windows Vista and Windows 7 guests. Up to 2x faster than Workstation 7.
  • Launch virtualized applications directly from the Windows 7 taskbar to create a seamless experience between applications in your virtual machines and the desktop.
  • Optimized performance for Intel’s Core i3, i5, i7 processor family for faster virtual machine encryption and decryption.
  • Support for more Host and Guest Operating Systems, including: Hosts: Windows 2008 R2, Ubuntu 10.04, RHEL 5.4, and more Guests: Fedora 12, Ubuntu 10.04, RHEL 5.4, SEL 11 SP1, and more.
  • Now includes built in Automatic Updates feature to check, download, and install VMware Workstation updates.
  • Ability to import and export Open Virtualization Format (OVF 1.0) packaged virtual machines and upload directly to VMware vSphere, the industry’s best platform for building cloud infrastructures.

    Download VMware Workstation HERE. You need a valid VMware Account to download.

  • Outlook 2007 Autodiscovery Warning when using SRV record for Autodiscover

    Sometimes when you open Outlook 2007 using a autodiscover srv record for Exchange 2007 you wil get de following error:

    autodiscover_warning_message 

    Solution 1:

    1. Close Outlook 2007
    2. Start Registry Editor
    3. In Windows 7, click Start –> RUN
    4. type regedit in de box and then click OK
    5. Collapse this imageExpand this image
    6. HKEY_CURRENT_USER\Software\Microsoft\Office\12.0\Outlook\AutoDiscover
    7. Click the Edit menu, point to New, and then click String Value.
    8. Type RedirectServers, and then press ENTER
    9. Right-click RedirectServers, and then click Modify.
    10. In the Value data box, type a semicolon delimited list of the HTTPS servers to which AutoDiscover can be redirected without prompting for confirmation from the user, and then click OK.
    For example, you want to allow for the following list of servers:
      – https://wardvissers.nl
      – https://wardvissers.local
    11.Type the following in the Value data box: wardvissers.local;wardvissers.nl
    12. On the File menu, click Exit to exit Registry Editor

    Solution 2:
    Setting the registry key with group policy preferences.
    clip_image002

    When trying to activate you get 0xC004F074 with description "The Key Management Server (KMS) is unavailable"

    Error:
    image

    The KMS host that is used is very probably a Windows Server 2008 KMS host that cannot standard activate Windows 7 and 2008 R2 machines.

    When you do not have Windows Server 2008 R2 KMS host key have then you must have a Volume License agreement so that your request your Windows 7 and Windows 2008 R2 kms keys.

    Resolution

    Step 1:
    -If the KMS host a Windows Server 2003 SP2 machine is you have the update from the KB article KB968915 install and restart the machine.
    -If the KMS host a Windows Server 2008 SP2 machine is you have the update from the KB article KB968912 install and start the new machine.
    -If the KMS host one Windows Server 2008 R2 machine is you have to install any further update.

    Step 2:
    You the new KMS host key import now. The commands are as follows:

    1. Uninstall KMS license Key on host – slmgr.vbs /upk

    2. Install Windows Server 2008 R2 KMS license key – slmgr.vbs /ipk <Your Key>

    3. Activate KMS server online: slmgr.vbs /ato

    4. Net Stop slsvc

    5. Net Start slsvc

    The clients can now activate

    Translate »