Desktop Virtualization for Dummies

Microsoft has released a free eBook: Desktop Virtualization for Dummies.
It has 43 pages with covers the following things
– What is Desktop Virtualization
– Discovering the benefits of Desktop Virtualization
– Thinking about your organization requirements
– Choosing between the options
– Taking things forward with Desktop Virtualization
– Ten (Well, Nearly) top tips for Desktop Virtualization

Click on the picture to download the pdf.
image

Source

Where to find the right MDT 2010 logs

Each MDT 2010 script automatically creates log files during its execution. The names of these log files match the name of the script—for example, ZTIGather.wsf creates a log file named ZTIGather.log. Each script also updates a common master log file (BDD.log) that aggregates the contents of the log files that MDT 2010 scripts create. MDT 2010 log files reside in C:\MININT\SMSOSD\OSDLOGS during the deployment process. Depending on the type of deployment being conducted, the log files are moved at the completion of the deployment to either %WINDIR%\SMSOSD or %WINDIR%\TEMP\SMSOSD. For Lite Touch Installation (LTI) deployments, the logs start in C:\MININT\SMSOSD\OSDLogs. They end up in %WINDIR%\TEMP\DeploymentLogs when task sequence execution is complete.

MDT 2010 creates the following log files:

BDD.log: This is the aggregated MDT 2010 log file that is copied to a network location at the end of the deployment if you specify the SLShare property in the Customsettings.ini file.

LiteTouch.log: This file is created during LTI deployments. It resides in %WINDIR%\TEMP\DeploymentLogs unless you specify the /debug:true option.

Scriptname.log: This file is created by each MDT 2010 script. Scriptname represents the name of the script in question.

SMSTS.log: This file is created by the Task Sequencer and describes all Task Sequencer transactions. Depending on the deployment scenario, it may reside in %TEMP%, %WINDIR%\System32\ccm\logs, or C:\_SMSTaskSequence, or C:\SMSTSLog.

Wizard.log: The deployment wizards create and update this file. 

WPEinit.log: This file is created during the Windows PE initialization process and is useful for troubleshooting errors encountered while starting Windows PE.

DeploymentWorkbench_id.log: This log file is created in the %temp% folder when you specify a /debug when starting the Deployment Workbench.

Configuring Client Access Array for Exchange 2010

When you want to use the Client Access Array function from Exchange 2010. You have to options.
1. Use the NLB function in Windows. Check this article that i blogged: Configuring NLB for Exchange 2010 for Cas load balancing.
2. When you have 2 physical load balancers in combination with a DAG cluster.

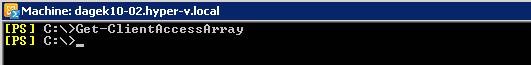
I haven’t any pre-Created CAS arrays in my hyper-v.local domain. But you would to check of there is any pre-created CAS Arrays. Run the command below. if you didn’t create a CAS Array before, you will get nothing .

Get-ClientAccessArray
clip_image002

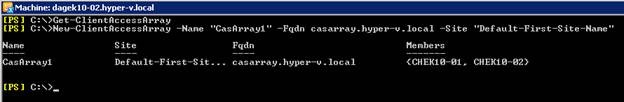
Then you should create new Client Access Array. Run below Cmdlet in Exchange Management Console

New-ClientAccessArray –Name “CasArray1” –Fqdn casarray.hyper-v.local -Site “Default-First-Site-Name”

clip_image004
Now we have finished creating a CAS array. Then we must associate databases with this CAS Array.
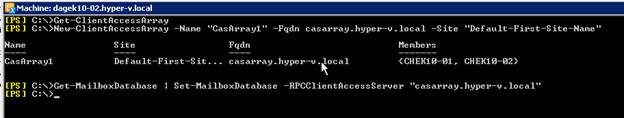
Use below CMDLet to add mailbox database to CAS array. We can attach all mailbox databases at once as shown as shown  below

Get-MailboxDatabase | Set-MailboxDatabase -RPCClientAccessServer “casarray.hyper-v.local”
clip_image006

Exchange 2010 SP1 Beta

Exchange Server 2010 Service Pack 1 Beta is available now. It incorporates a number of feature updates including: archiving and discovery enhancements, a faster Outlook Web App (OWA), upgraded mobility features, and several improvements in the management UI. In short it helps you achieve new levels of reliability and performance by delivering features that help to simplify your administration, protect your communications, and delight your customers by meeting their demands for greater business mobility.

Microsoft Download Center Link is here and direct downloadable exe file link is available below.

File Name: Exchange2010-SP1-Beta-x64.exe
Version: 14.01.0180.002
Date Published: 6/5/2010
Language: English
Download Size: 532.5 MB

Configuring NLB for Exchange 2010 for CAS Load Balancing

Exchange’s dependence on the Client Access Server (CAS) role has increased dramatically in Exchange 2010.  This is because, in Exchange 2010, on-network Outlook MAPI connectivity now connects to a mailbox through the CAS role via the RPC Client Access Service.  As a result, high availability of the CAS role is crucial since any failure of CAS could affect Outlook client connectivity.  For smaller implementations or those where the limitations of native Windows Network Load Balancing (NLB) are not a major problem

You need two or more Exchange 2010 servers (each with two NICs) with the CAS role installed have been deployed, you are ready to start configuring NLB to provide high availability and load balancing.  First, you must allocate a dedicated private IP address and create an associated A record in DNS for the NLB cluster. 

This IP address and name are what clients will connect to and against which the ClientAccessArray will be created.  In this blog post, I will use 192.168.150.95 and casarray.hyper-v.local
To simplify the management of your NLB cluster members, I recommend that you name each NIC’s network connection so that it is easy to understand what function the NIC serves.  For example, as depicted below, I have named the connections “LAN” (used for communication with clients and servers on the network) and “NLB” (used for internal NLB heartbeat).  This process should be repeated on all NLB cluster members.

IP configuration:
Server 1:
LAN:
IP: 192.168.150.90
Subnetmask: 255.255.255.0
Gateway: 192.168.150.254
DNS: 192.168.150.1

Server 2:
LAN:
IP: 192.168.150.91
Subnetmask: 255.255.255.0
Gateway: 192.168.150.254
DNS: 192.168.150.1
clip_image002


Configuring NLB – First Member

On each NLB cluster member, NLB must be installed.  With Windows 2008 R2, this can be completed simply by running the command “ServerManagerCmd -i NLB” via a command prompt.  Once NLB has been installed, launch the Network Load Balancing Manager to continue the configuration process.

clip_image003[1]

To create your new cluster, you can right-click Network Load Balancing Clusters or simply click Cluster, New.  In the New Cluster wizard, enter the name of the first server in the NLB cluster (for example, CHEK10-01) and click Connect.  This will display the available NICs on the server, at which point the NLB NIC should be chosen before clicking Next.

clip_image005

Since this is the first member of the NLB cluster, you can leave the all of the Host Parameters at their default values, as depicted below.  Please note that the Priority value should be configured as 1 for the first member.

clip_image007

Next we must configure the IP address and subnet mask of the NLB cluster, which is the IP address for which we created a DNS A record at the very beginning of this process.  In this example, this would be 192.168.150.95 and 255.255.255.0, respectively.

clip_image009

For the Cluster Parameters, we want to enter the FQDN of the DNS A record we created at the very beginning of this process (casarray.hyper-v.local).  In addition, Unicast should be selected as the desired clustered operation mode.

clip_image011

I lieve the Port Rules how they are and end with Finish
clip_image013

Let the NLB cluster converge with its first member and you should eventually see the cluster report success.

clip_image015[1]

Now you can proceed with adding your second cluster member.

Configuring NLB – Second/Subsequent Member

After the configuration of the NLB cluster itself and the first NLB cluster member has been completed, you are ready to add additional members.  Provided that NLB has been installed, you can simply right-click on your NLB cluster in the Network Load Balancing Manager and click Add Host To Cluster.

Enter the name of the second NLB cluster member, for example CHEK10-02, and click Connect.  Be sure to choose the NLB LAN NIC and click Next.

clip_image017

On the Host Parameters screen, ensure that the Priority is set to 2 (or as appropriate, depending on how many cluster members you have) and click Next.

clip_image019

Confirm that your port rules are accurate and, if they are, click Finish to add your second NLB cluster member.

clip_image021

Let the NLB cluster converge with the new member and, eventually, it should report success.

clip_image023

At this point, you have an NLB cluster with two members!

Next configure CASARRAY.

Hyper-V Live Migration with HP StorageWorks

The video demonstrates Long Distance Live Migration with a 8 node Microsoft Hyper-V cluster that is achieved with the HP StorageWorks EVA

Access Denied Error 0x80070005 message when initializing TPM for Bitlocker

When you try to turn on Bitlocker on Windows 7 Operating System Drive, you may get the Access Denied Error message while initializing TPM.

image

Additionally, when you open the TPM Management Console and you try to initialize TPM you get error message 0x80070005.

image

Solution:

To set correct permissions, follow the instruction below:

1. Open Active Directory Users and Computers.

2. Select the OU where you have all computers which will have Bitlocker turned ON.

3. Right Click on the OU and click Delegate Control.

image

4. Click Next and then click Add.

image

image

5. Type SELF as the Object Name.

image

6. Select create a custom task to delegate.

image

7. From the object in the folder, select Computer Objects.

image

8. Under show these permissions, select all 3 checkbox.

image

9. Scroll down in permissions and select the attribute Write msTPM-OwnerInformation.

image

10. Click Finish.
image

After you have done the above steps, you should be able to initialize TPM successfully.

It worked for me!!!

SOURCE

Exchange 2010 Hiding a Distribution Group from the Exchange Address List

Some times you want to hide a Distribution Group from de Global Address List (GAL).
In Exchange 2010 this is a simple thing
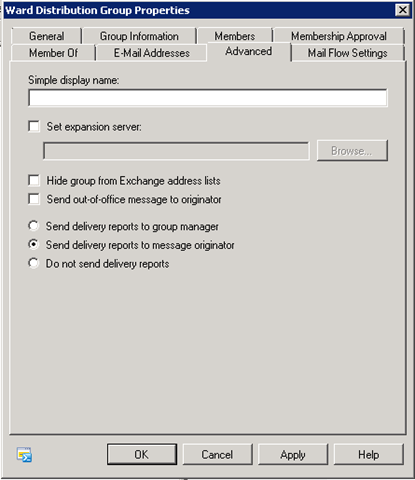
1. Open the properties from the Distribution Group.

2. Go to the Tab Advanced
image

3. Set V by Hide group from Exchange address list

image

Certificate Manager for Exchange 2007

Exchange 2007 enables SSL within IIS by default. Using PowerShell commands, certificate creation and management is quite confusing and often results with incorrect results due to the nature of the syntax. U-BTech Solutions is providing Certificate Manager for Exchange Server 2007 freely, to ease the process with a simple, easy to use GUI which enables you to:

1) Manage your current server certificates.
2) Enable certificates for Exchange 2007 Services (POP, IMAP, SMTP, IIS, UM).
3) Generate an Exchange 2007 Certificate Signing Request and process the Certificate Authority answer.
4) Generate an Exchange 2007 Self-Signed certificate (not for production use).
5) Easily include additional subject names in a single certificate.
6) Import & Export ability for existing certificates.
To read more about Certificate Use in Exchange 2007 at Microsoft TechNet follow the link:

Certificate Manager for Exchange Server 2007 is currently offered by U-BTech Solutions free of charge

certificate-manager-main-menu[1]

Certificate Manager for Exchange Server 2007 Flash Demonstration

Download – Certificate Manager for Exchange 2007

SOURCE

Microsoft Remote Desktop Connection Manager for Free

Microsoft has released a new free tool named Remote Desktop Connection Manager.
image 

Features:
– You can set user, password and domain on a group and every server in that group you add they inherit the same settings this is very handy when you have a lot of servers.
– Bulk import servers is possible with txt files.
– Export the settings

You can Download Remote Desktop Connection Manager Here

Translate »